7B
推荐solaudit-coder:7b
速度与准确率兼顾
适合日常 PR 审查和 CI 流水线的默认模型。基于代码专用基座,对 Solidity 语法理解深入。
- 基座
- qwen2.5-coder:7b
- 大小
- 4.7 GB
- 上下文
- 32K
- 推荐配置
- 内存 8GB · GPU 可选
准确率78
速度88
ollama create solaudit-coder:7bSolAudit AI 是一套专为 Solidity 安全审计打造的开源 LLM 模型。它们通过 Ollama 仅在你的电脑上运行,代码不会外传,并以 JSON 报告的形式返回重入、访问控制、预言机操纵等漏洞。
❯ curl -s -X POST https://solauditai.dev/api/audit -H "Content-Type: text/plain" --data-binary @Vault.sol | jq .report
⠿ solaudit-coder:7b 分析中… 212 lines · 2.8s
CRITICAL Reentrancy in withdraw() SWC-107 · L16
HIGH tx.origin used for authorization SWC-115 · L22
LOW Missing events for state changes L10, L18
risk_score: 94 / 100
Models
所有模型均以 Ollama Modelfile 形式提供:在成熟的开源代码 LLM 之上,叠加 Solidity 审计专用的系统提示词和参数。
速度与准确率兼顾
适合日常 PR 审查和 CI 流水线的默认模型。基于代码专用基座,对 Solidity 语法理解深入。
ollama create solaudit-coder:7b基于逐步推理的深度分析
逐步推理调用流程和状态变化,发现重入、价格操纵等复合型漏洞。
ollama create solaudit-deep:14b主网部署前的最终检查
面向大型协议和多合约代码库的旗舰模型,误报率最低。
ollama create solaudit-pro:32b笔记本也能轻松运行
适合快速初筛和学习用途的轻量模型,也非常适合在编辑器保存时即时检查。
ollama create solaudit-lite:3b* 准确率和速度仅为模型间相对比较的参考指标,实际性能取决于硬件和代码库。
How it works
无需云端 API 密钥,也没有按量计费。终端 → Ollama → 安全报告,只需三步。
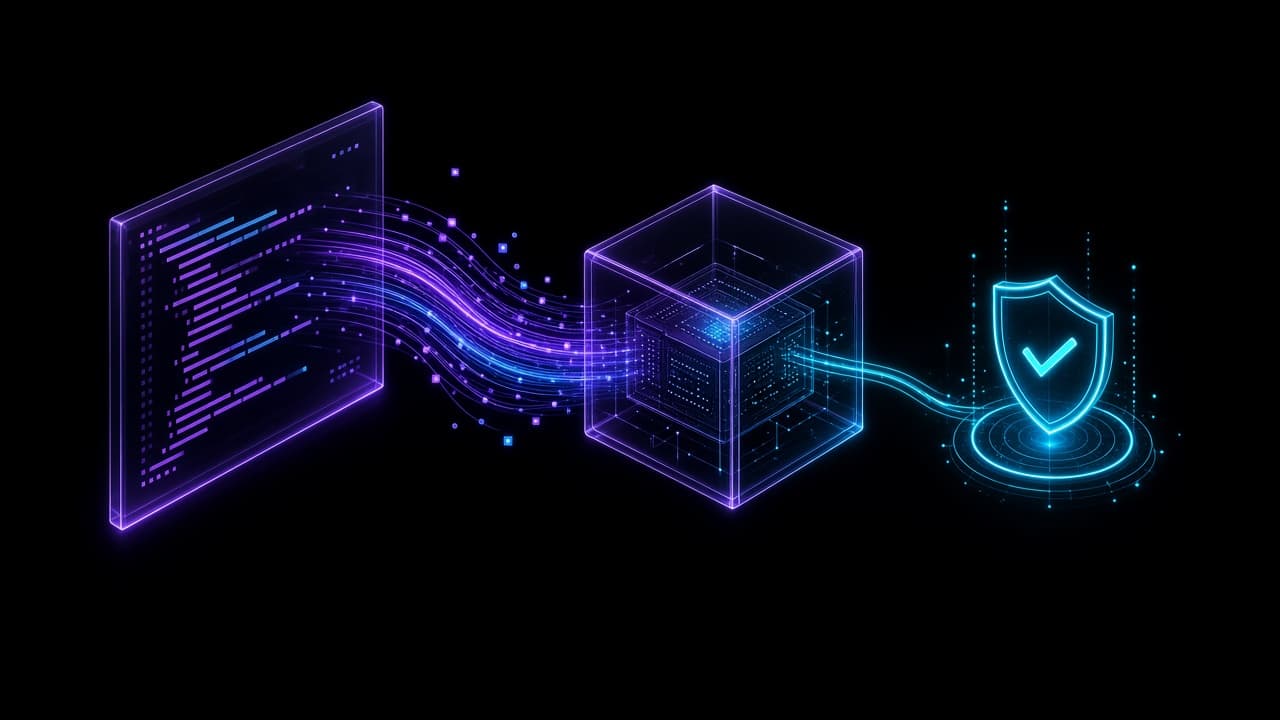
用 curl 直接发送 .sol 文件。同时支持本地 Ollama API(:11434)和本站的 /api/audit 代理。
curl --data-binary @Vault.solOllama 在你的 GPU/CPU 上运行审计模型,系统提示词按照基于 SWC Registry 的检查清单分析代码。
ollama · temperature 0.1返回包含严重程度、位置、SWC ID 和修复建议的结构化 JSON,可直接接入 jq、CI 和仪表盘。
format: "json"
Why local AI
SolAudit AI 是专业审计之前的第一道防线,能快速筛出常见错误。在开发循环中即时获得反馈。
即使是未公开的协议代码也可放心分析。所有推理都只在本地 Ollama 运行时中进行。
没有按 Token 计费,每次提交、每个文件想审计多少次都不花钱。
借助 Ollama 的 JSON 模式,始终获得相同结构的报告。无需担心解析错误,轻松实现自动化。
只需 curl 和 jq,就能在 GitHub Actions、GitLab CI 中发现 critical 漏洞时让构建失败。
Quick start · curl
选择模型和操作系统后,下方命令会自动更新。只需复制并按顺序粘贴即可。
安装本地 LLM 运行时 Ollama。安装完成后,服务会在后台通过 :11434 端口自动运行。
curl -fsSL https://ollama.com/install.sh | sh

# 验证安装(如果服务未运行:ollama serve)
ollama --version
curl http://localhost:11434/api/versionsolaudit-coder:7b 基于 qwen2.5-coder:7b(4.7 GB)构建。
ollama pull qwen2.5-coder:7b用 curl 下载 Modelfile(审计系统提示词 + 参数),并注册为 Ollama 模型。
curl -fsSL https://solauditai.dev/api/modelfile/solaudit-coder-7b -o solaudit-coder-7b.Modelfile
ollama create solaudit-coder:7b -f solaudit-coder-7b.Modelfile

ollama list | grep solaudit直接向 Ollama 的 /api/generate 发送代码片段。format: "json" 可确保返回结构化报告。
curl http://localhost:11434/api/generate -d '{
  "model": "solaudit-coder:7b",
  "prompt": "contract A { function kill() public { selfdestruct(payable(msg.sender)); } }",
  "format": "json",
  "stream": false
}' | jq -r '.response | fromjson'用 jq -Rs 将文件内容安全地封装为 JSON 字符串,并通过管道发送到 /api/chat。
jq -Rs '{
  model: "solaudit-coder:7b",
  stream: false,
  format: "json",
  messages: [{ role: "user", content: . }]
}' Vault.sol \
  | curl -s http://localhost:11434/api/chat -d @- \
| jq -r '.message.content | fromjson'用 npm run dev 启动本站后,/api/audit 会替你调用 Ollama。无需 JSON 转义,直接发送 .sol 文件即可。
curl -s -X POST "https://solauditai.dev/api/audit?model=solaudit-coder:7b" \
  -H "Content-Type: text/plain" \
  --data-binary @Vault.sol | jq .

# 实时流式输出 (NDJSON)
curl -N -X POST "https://solauditai.dev/api/audit?model=solaudit-coder:7b&stream=true" \
  -H "Content-Type: text/plain" \
  --data-binary @Vault.sol
Live example
使用 solaudit-coder:7b 审计一个暗藏经典重入漏洞和 tx.origin 认证缺陷的 Vault 合约的结果。
输入 · Vault.sol
1// SPDX-License-Identifier: MIT2pragma solidity ^0.8.20;34contract Vault {5 mapping(address => uint256) public balances;6 address public owner;78 constructor() { owner = msg.sender; }910 function deposit() external payable {11 balances[msg.sender] += msg.value;12 }1314 function withdraw() external {15 uint256 amount = balances[msg.sender];16 (bool ok, ) = msg.sender.call{value: amount}("");17 require(ok, "transfer failed");18 balances[msg.sender] = 0;19 }2021 function sweep(address to) external {22 require(tx.origin == owner, "not owner");23 payable(to).transfer(address(this).balance);24 }25}输出 · POST /api/audit
{
  "model": "solaudit-coder:7b",
  "duration_ms": 2814,
  "report": {
    "summary": "Vault is exposed to reentrancy and phishing-based owner takeover. Funds can be fully drained.",
    "risk_score": 94,
    "findings": [
      {
        "id": "SA-001",
        "title": "Reentrancy in withdraw()",
        "severity": "critical",
        "swc": "SWC-107",
        "location": "withdraw() L16-18",
        "description": "External call is made before the balance is zeroed, allowing a malicious receiver to re-enter and withdraw repeatedly.",
        "recommendation": "Apply Checks-Effects-Interactions: set balances[msg.sender] = 0 before the call, or use ReentrancyGuard."
      },
      {
        "id": "SA-002",
        "title": "tx.origin used for authorization",
        "severity": "high",
        "swc": "SWC-115",
        "location": "sweep() L22",
        "description": "A contract called by the owner can invoke sweep() and pass the tx.origin check.",
        "recommendation": "Replace tx.origin with msg.sender and consider OpenZeppelin Ownable."
      },
      {
        "id": "SA-003",
        "title": "Missing events for state changes",
        "severity": "low",
        "swc": null,
        "location": "deposit() L10, withdraw() L18",
        "description": "Deposits and withdrawals emit no events, hindering off-chain monitoring.",
        "recommendation": "Emit Deposit and Withdraw events."
      }
    ],
    "gas_optimizations": ["Declare owner as immutable", "Use custom errors instead of revert strings"]
  }
}
Coverage
从经典漏洞到 DeFi 特有的攻击向量,再到 Gas 优化建议,一次请求全部检查。
外部调用后才更新状态导致的重复提款
缺失 onlyOwner、未受保护的 selfdestruct
对不可信目标的 delegatecall
依赖现货价格、闪电贷价格操纵
通过钓鱼合约夺取权限
忽略底层 call 的失败
unchecked 代码块或 0.8 以下版本的算术运算
缺少 nonce·chainId 的签名重放
可升级代理的存储布局冲突
交易顺序依赖、未设置滑点
基于 block.timestamp / blockhash 的随机数
无界循环、外部调用 revert 导致的停摆
API reference
直接调用 Ollama(http://localhost:11434),或通过 SolAudit 代理(https://solauditai.dev)更简单地调用。
/api/audit接收 Solidity 源码,经 Ollama 审计后返回 JSON 报告SolAudit/api/models可用模型列表及 Modelfile 下载地址SolAudit/api/modelfile/:slug用于 ollama create 的 Modelfile (text/plain)SolAudit/api/chat对话式请求 — 通过 messages 数组传入合约Ollama/api/generate单提示词请求 — 用于测试简短代码片段Ollama| 名称 | 类型 | 位置 | 说明 |
|---|---|---|---|
| code | string | JSON 请求体 | Solidity 源代码(text/plain 请求时为整个请求体) |
| model | string | body · query | 要使用的模型,默认为 solaudit-coder:7b |
| stream | boolean | body · query | 为 true 时原样转发 Ollama 的 NDJSON 流 |
使用 JSON 请求体
curl -s https://solauditai.dev/api/audit \
  -H "Content-Type: application/json" \
  -d '{
    "model": "solaudit-pro:32b",
    "code": "pragma solidity ^0.8.20; contract T { function f() external { selfdestruct(payable(msg.sender)); } }"
  }'
CI 流水线关卡
# 发现 critical / high 漏洞时让 CI 失败 (exit 1)
for f in contracts/*.sol; do
  curl -s -X POST "https://solauditai.dev/api/audit" \
    -H "Content-Type: text/plain" --data-binary @"$f" \
  | jq -e '[.report.findings[] | select(.severity=="critical" or .severity=="high")] | length == 0' \
  || { echo "❌ $f"; exit 1; }
done
FAQ
不能。SolAudit AI 是在开发阶段快速筛查常见错误的初步工具。LLM 可能存在误报和漏报,因此涉及真实资金的合约,务必同时进行 Slither、Foundry 模糊测试等静态/动态分析,并交由专业审计机构审查。
直接调用 Ollama(localhost:11434)时,代码不会离开你的电脑。使用 /api/audit 代理时,代码也只会在本 Next.js 服务器与 OLLAMA_HOST 指定的 Ollama 服务器之间传输。
可以。Ollama 仅靠 CPU 也能运行,但速度较慢,因此没有 GPU 时推荐使用 solaudit-lite:3b 或 solaudit-coder:7b。Apple Silicon Mac 会自动启用 Metal 加速。
可以。在请求消息中加上 "Write description and recommendation in Chinese" 之类的语句,或在 Modelfile 的 SYSTEM 提示词末尾加入中文输出规则,然后重新执行 ollama create。
按文件拆分、控制在模型上下文(16K–32K Token)以内发送最为准确。可以像 API 部分的 CI 脚本那样循环处理 contracts/*.sol,或将 forge flatten 的结果发送给 solaudit-pro:32b。
在 .env.local 中设置 OLLAMA_HOST=http://<服务器 IP>:11434,并在服务器上用 OLLAMA_HOST=0.0.0.0 ollama serve 启动。对外公开时,务必添加反向代理和身份验证。