7B
추천solaudit-coder:7b
속도와 정확도의 균형
일상적인 PR 리뷰와 CI 파이프라인에 적합한 기본 모델. 코드 특화 베이스로 Solidity 문법 이해도가 높습니다.
- Base
- qwen2.5-coder:7b
- 크기
- 4.7 GB
- Context
- 32K
- 권장 사양
- RAM 8GB · GPU 선택
정확도78
속도88
ollama create solaudit-coder:7bSolAudit AI는 Solidity 보안 감사에 특화된 오픈 LLM 모델 모음입니다. Ollama 위에서 내 컴퓨터로만 실행되어 코드가 외부로 나가지 않고, 재진입·접근 제어·오라클 조작 같은 취약점을 JSON 리포트로 돌려줍니다.
❯ curl -s -X POST https://solauditai.dev/api/audit -H "Content-Type: text/plain" --data-binary @Vault.sol | jq .report
⠿ solaudit-coder:7b 분석 중… 212 lines · 2.8s
CRITICAL Reentrancy in withdraw() SWC-107 · L16
HIGH tx.origin used for authorization SWC-115 · L22
LOW Missing events for state changes L10, L18
risk_score: 94 / 100
Models
모든 모델은 검증된 오픈소스 코드 LLM 위에 Solidity 감사용 시스템 프롬프트와 파라미터를 입힌 Ollama Modelfile로 제공됩니다.
속도와 정확도의 균형
일상적인 PR 리뷰와 CI 파이프라인에 적합한 기본 모델. 코드 특화 베이스로 Solidity 문법 이해도가 높습니다.
ollama create solaudit-coder:7b단계별 추론 기반 심층 분석
호출 흐름과 상태 변화를 단계적으로 추론해 재진입·가격 조작 같은 복합 취약점을 찾아냅니다.
ollama create solaudit-deep:14b메인넷 배포 전 최종 점검용
대형 프로토콜, 다중 컨트랙트 코드베이스를 위한 플래그십 모델. 가장 낮은 오탐률을 제공합니다.
ollama create solaudit-pro:32b노트북에서도 가볍게
빠른 1차 스캔과 교육용으로 적합한 경량 모델. 에디터 저장 시 즉시 검사하는 용도로 쓰기 좋습니다.
ollama create solaudit-lite:3b* 정확도/속도는 모델 간 상대 비교를 위한 참고 지표이며, 실제 성능은 하드웨어와 코드베이스에 따라 달라집니다.
How it works
클라우드 API 키도, 사용량 과금도 없습니다. 터미널 → Ollama → 보안 리포트, 세 단계가 전부입니다.
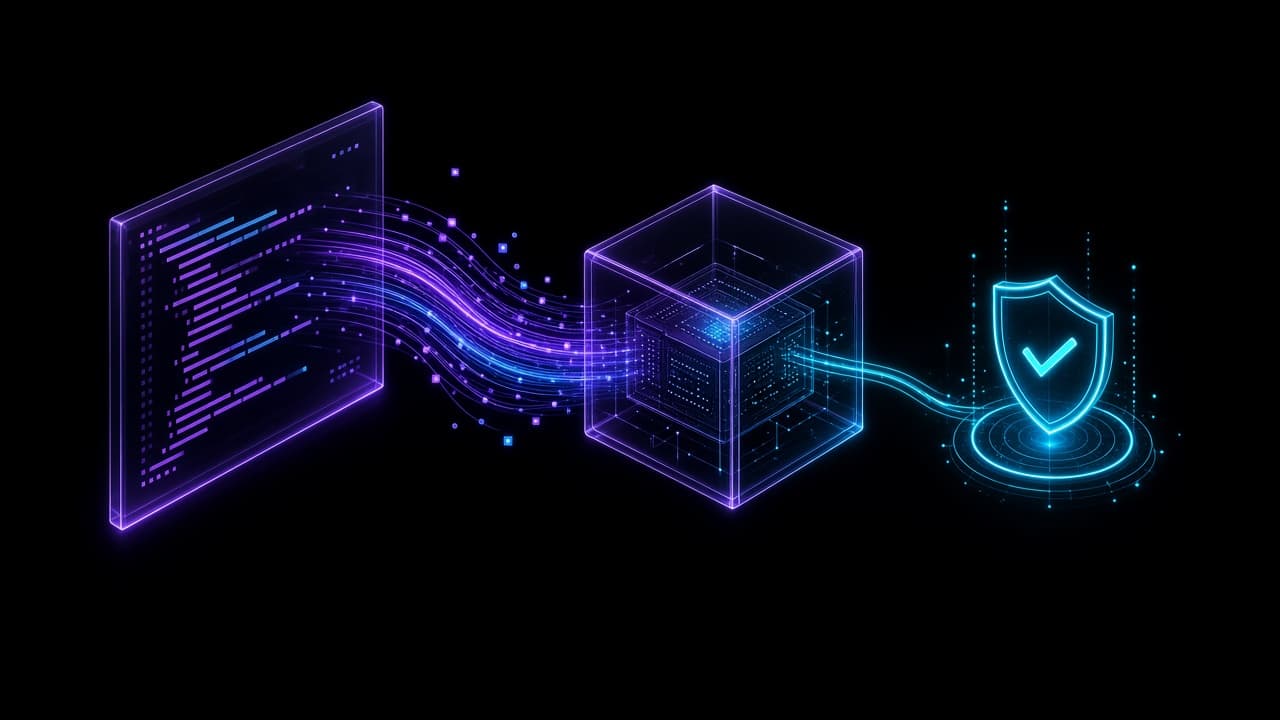
curl로 .sol 파일을 그대로 보냅니다. 로컬 Ollama API(:11434) 또는 이 사이트의 /api/audit 프록시 모두 지원합니다.
curl --data-binary @Vault.solOllama가 내 GPU/CPU에서 감사 모델을 실행합니다. 시스템 프롬프트가 SWC 레지스트리 기반 체크리스트로 코드를 분석합니다.
ollama · temperature 0.1심각도·위치·SWC ID·수정 방법이 담긴 구조화된 JSON을 반환해 jq, CI, 대시보드에 바로 연결할 수 있습니다.
format: "json"
Why local AI
SolAudit AI는 전문 감사 전 단계에서 흔한 실수를 빠르게 걸러내는 1차 방어선입니다. 개발 루프 안에서 즉시 피드백을 받으세요.
미공개 프로토콜 코드도 안심하고 분석하세요. 모든 추론은 로컬 Ollama 런타임에서만 일어납니다.
토큰 과금이 없으니 커밋마다, 파일마다 원하는 만큼 감사를 돌려도 비용이 들지 않습니다.
Ollama의 JSON 모드로 항상 같은 스키마의 리포트를 받습니다. 파싱 에러 걱정 없이 자동화하세요.
curl과 jq만 있으면 GitHub Actions, GitLab CI에서 critical 발견 시 빌드를 실패시킬 수 있습니다.
Quick start · curl
모델과 운영체제를 고르면 아래 명령어가 자동으로 바뀝니다. 복사해서 순서대로 붙여넣기만 하세요.
로컬 LLM 런타임인 Ollama를 설치합니다. 설치 후 백그라운드에서 :11434 포트로 서버가 자동 실행됩니다.
curl -fsSL https://ollama.com/install.sh | sh

# 설치 확인 (서버가 꺼져 있다면: ollama serve)
ollama --version
curl http://localhost:11434/api/versionsolaudit-coder:7b 모델은 qwen2.5-coder:7b (4.7 GB) 위에 만들어집니다.
ollama pull qwen2.5-coder:7bcurl로 Modelfile(감사 시스템 프롬프트 + 파라미터)을 내려받아 Ollama 모델로 등록합니다.
curl -fsSL https://solauditai.dev/api/modelfile/solaudit-coder-7b -o solaudit-coder-7b.Modelfile
ollama create solaudit-coder:7b -f solaudit-coder-7b.Modelfile

ollama list | grep solauditOllama의 /api/generate에 코드 조각을 직접 넣어 봅니다. format: "json"이 구조화된 리포트를 보장합니다.
curl http://localhost:11434/api/generate -d '{
  "model": "solaudit-coder:7b",
  "prompt": "contract A { function kill() public { selfdestruct(payable(msg.sender)); } }",
  "format": "json",
  "stream": false
}' | jq -r '.response | fromjson'jq -Rs로 파일 내용을 안전하게 JSON 문자열로 감싸 /api/chat에 파이프합니다.
jq -Rs '{
  model: "solaudit-coder:7b",
  stream: false,
  format: "json",
  messages: [{ role: "user", content: . }]
}' Vault.sol \
  | curl -s http://localhost:11434/api/chat -d @- \
| jq -r '.message.content | fromjson'이 사이트를 npm run dev로 띄우면 /api/audit가 Ollama를 대신 호출합니다. JSON 이스케이프 없이 .sol 파일을 그대로 보내세요.
curl -s -X POST "https://solauditai.dev/api/audit?model=solaudit-coder:7b" \
  -H "Content-Type: text/plain" \
  --data-binary @Vault.sol | jq .

# 실시간 스트리밍 (NDJSON)
curl -N -X POST "https://solauditai.dev/api/audit?model=solaudit-coder:7b&stream=true" \
  -H "Content-Type: text/plain" \
  --data-binary @Vault.sol
Live example
고전적인 재진입(Reentrancy)과 tx.origin 인증 버그가 숨어 있는 Vault 컨트랙트를 solaudit-coder:7b로 감사한 결과입니다.
입력 · Vault.sol
1// SPDX-License-Identifier: MIT2pragma solidity ^0.8.20;34contract Vault {5 mapping(address => uint256) public balances;6 address public owner;78 constructor() { owner = msg.sender; }910 function deposit() external payable {11 balances[msg.sender] += msg.value;12 }1314 function withdraw() external {15 uint256 amount = balances[msg.sender];16 (bool ok, ) = msg.sender.call{value: amount}("");17 require(ok, "transfer failed");18 balances[msg.sender] = 0;19 }2021 function sweep(address to) external {22 require(tx.origin == owner, "not owner");23 payable(to).transfer(address(this).balance);24 }25}출력 · POST /api/audit
{
  "model": "solaudit-coder:7b",
  "duration_ms": 2814,
  "report": {
    "summary": "Vault is exposed to reentrancy and phishing-based owner takeover. Funds can be fully drained.",
    "risk_score": 94,
    "findings": [
      {
        "id": "SA-001",
        "title": "Reentrancy in withdraw()",
        "severity": "critical",
        "swc": "SWC-107",
        "location": "withdraw() L16-18",
        "description": "External call is made before the balance is zeroed, allowing a malicious receiver to re-enter and withdraw repeatedly.",
        "recommendation": "Apply Checks-Effects-Interactions: set balances[msg.sender] = 0 before the call, or use ReentrancyGuard."
      },
      {
        "id": "SA-002",
        "title": "tx.origin used for authorization",
        "severity": "high",
        "swc": "SWC-115",
        "location": "sweep() L22",
        "description": "A contract called by the owner can invoke sweep() and pass the tx.origin check.",
        "recommendation": "Replace tx.origin with msg.sender and consider OpenZeppelin Ownable."
      },
      {
        "id": "SA-003",
        "title": "Missing events for state changes",
        "severity": "low",
        "swc": null,
        "location": "deposit() L10, withdraw() L18",
        "description": "Deposits and withdrawals emit no events, hindering off-chain monitoring.",
        "recommendation": "Emit Deposit and Withdraw events."
      }
    ],
    "gas_optimizations": ["Declare owner as immutable", "Use custom errors instead of revert strings"]
  }
}
Coverage
고전적인 버그부터 DeFi 특화 공격 벡터, 가스 최적화 제안까지 한 번의 요청으로 점검합니다.
외부 호출 후 상태 갱신으로 인한 반복 출금
누락된 onlyOwner, 무방비 selfdestruct
신뢰할 수 없는 대상으로의 delegatecall
스팟 가격 의존, 플래시론 가격 조작
피싱 컨트랙트를 통한 권한 탈취
low-level call 실패 무시
unchecked 블록, <0.8 버전의 산술 연산
nonce·chainId 없는 서명 재사용
업그레이드 프록시의 스토리지 레이아웃 충돌
트랜잭션 순서 의존, 슬리피지 미설정
block.timestamp / blockhash 기반 난수
무제한 루프, 외부 호출 revert로 인한 정지
API reference
Ollama(http://localhost:11434)를 직접 호출하거나, SolAudit 프록시(https://solauditai.dev)로 더 간단하게 호출하세요.
/api/auditSolidity 소스를 받아 Ollama로 감사 후 JSON 리포트 반환SolAudit/api/models제공 모델 목록과 Modelfile 다운로드 URLSolAudit/api/modelfile/:slugollama create 에 사용할 Modelfile (text/plain)SolAudit/api/chat대화형 요청 — messages 배열로 컨트랙트 전달Ollama/api/generate단일 프롬프트 요청 — 짧은 코드 조각 테스트용Ollama| 이름 | 타입 | 위치 | 설명 |
|---|---|---|---|
| code | string | JSON body | Solidity 소스 코드 (text/plain 요청이면 본문 전체) |
| model | string | body · query | 사용할 모델. 기본값 solaudit-coder:7b |
| stream | boolean | body · query | true면 Ollama NDJSON 스트림을 그대로 전달 |
JSON 본문으로 요청
curl -s https://solauditai.dev/api/audit \
  -H "Content-Type: application/json" \
  -d '{
    "model": "solaudit-pro:32b",
    "code": "pragma solidity ^0.8.20; contract T { function f() external { selfdestruct(payable(msg.sender)); } }"
  }'
CI 파이프라인 게이트
# critical / high 취약점이 있으면 CI 실패 (exit 1)
for f in contracts/*.sol; do
  curl -s -X POST "https://solauditai.dev/api/audit" \
    -H "Content-Type: text/plain" --data-binary @"$f" \
  | jq -e '[.report.findings[] | select(.severity=="critical" or .severity=="high")] | length == 0' \
  || { echo "❌ $f"; exit 1; }
done
FAQ
아니요. SolAudit AI는 개발 단계에서 흔한 실수를 빠르게 걸러내는 1차 도구입니다. LLM은 오탐과 미탐이 있을 수 있으므로, 실제 자금을 다루는 컨트랙트는 반드시 Slither·Foundry 퍼징 같은 정적/동적 분석과 전문 감사 업체의 리뷰를 함께 거치세요.
Ollama(localhost:11434)를 직접 호출하면 코드가 내 컴퓨터를 벗어나지 않습니다. /api/audit 프록시를 쓸 때도 이 Next.js 서버와 OLLAMA_HOST로 지정한 Ollama 서버 사이에서만 오갑니다.
네. Ollama는 CPU만으로도 동작합니다. 다만 속도가 느려지므로 GPU가 없다면 solaudit-lite:3b 또는 solaudit-coder:7b를 권장합니다. Apple Silicon Mac은 Metal 가속이 자동으로 적용됩니다.
가능합니다. 요청 메시지에 "Write description and recommendation in Korean" 같은 문장을 추가하거나, Modelfile의 SYSTEM 프롬프트 마지막에 한국어 출력 규칙을 넣고 ollama create 로 다시 생성하세요.
모델의 컨텍스트(16K–32K 토큰)에 맞게 파일 단위로 나눠 보내는 것이 가장 정확합니다. API 섹션의 CI 스크립트처럼 contracts/*.sol을 반복 처리하거나, forge flatten 결과를 solaudit-pro:32b에 보내세요.
.env.local에 OLLAMA_HOST=http://<서버 IP>:11434 를 설정하고 서버에서는 OLLAMA_HOST=0.0.0.0 ollama serve 로 실행하세요. 외부에 노출할 때는 리버스 프록시와 인증을 반드시 추가하세요.